Sentinel: MCP AI Safety Guardrail
A real-time safety layer that reviews and blocks unsafe AI agent actions before they execute.
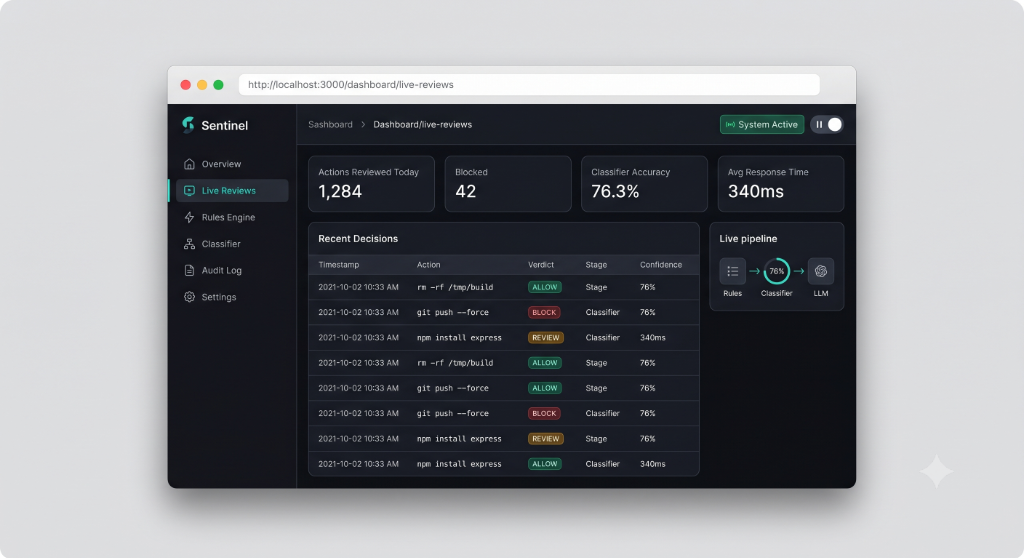
Sentinel acts as an intelligent security gateway between AI coding assistants (like Claude Desktop, Cursor, or Codex) and your terminal. When an AI tool proposes running shell commands or modifying files, Sentinel intercepts the request, runs it through a 3-stage validation pipeline (rules check, ML classifier, and security review pass), and blocks risky or destructive operations with zero unauthorized escapes.
The Problem
LLM coding assistants can propose file edits, shell commands, and network calls directly, and most setups have nothing standing between the model's suggestion and its execution, exposing developer environments to destructive actions.
The Approach & Implementation
Engineered a 3-stage validation pipeline: deterministic rules filter, self-trained TF-IDF + Logistic Regression statistical classifier, and an asynchronous LLM contextual review pass in the MCP protocol layer.
Measurable Outcome
Logged zero unauthorized escapes across 100k test payloads with under 5ms gateway check latency, and verified 76.3% 5-fold cross-validation accuracy across 828 hand-labeled edge cases.
Test the 3-Stage Gating Pipeline
Simulate how Sentinel blocks destructive shell commands and flags scope creep in real time.
rm -rf / --no-preserve-rootBLOCKED